#blockchain security
Bitget Hit by $387M Crypto Exploit

Crypto exchange Bitget has suffered a security breach that has reportedly drained over $380 million from the exchange and is on track to be the largest crypto exploit this year.
The exploit, which is said to have happened around 6:31 p.m. UTC on Sept. 24, involved transfers from some of the exchange’s hot wallets.

According to Gracy Chen, Bitget’s CEO, the hack occurred as a result of attackers compromising a critical backend system within the exchange’s wallet infrastructure, using this compromise to spoof transaction data and trigger the authorization process to move funds.
Although this hack now ranks as the largest crypto hack of the year, Bitget said that the incident fell within the coverage of its User Protection Fund, which currently holds more than $464 million, confirming that customers’ funds and deposits on the exchange were intact.
Bitget’s Response
Following the detection of the unauthorized withdrawals, the security team at the exchange swiftly activated an emergency response, temporarily suspending withdrawals while the team conducted a comprehensive security review of the incident.
The team also said it started working with third-party security experts Mandiant and SlowMist for a full investigation, while also providing updates about the incident, with the exchange’s CEO going on a live Q&A session on X about the incident.
Bitget also launched a bounty program, mobilizing exchanges and other security experts who can assist with freezing and recovering the stolen assets. So far, stablecoin issuers Tether and Circle have frozen roughly $318,000 worth of stablecoins in wallets said to be involved in the exploit, leaving a large majority of the funds still under the control of the attacker.
Bitget’s exploit is coming at a time when Evercrest Technologies, the company behind liquid staking protocol KelpDAO, is suing LayerZero for its alleged negligence that led to attackers exploiting the protocol for $292 million in April of this year.
According to a lawsuit filed against the protocol and its CEO, KelpDAO alleges that LayerZero reviewed and endorsed in writing its single verifier (1-of-1 DVN) cross-chain bridge infrastructure, which was eventually used by attackers to exploit the protocol.
Blockworks Launches Agentic Feature for Real-Time Crypto Alerts

Blockworks, the crypto data and intelligence company, has introduced the Agentic Detection feature to Blockworks Monitoring, its surveillance product that sends crypto alerts in real time.
Through this feature, all Blockworks customers using the surveillance product will be able to receive crypto alerts as soon as the agents detect them, in real time and without the need for a review by a security analyst.

The crypto alerts sent to teams will include information about the security incident, the assets and organisations involved in the incident, and the source of the information. This will allow customers to verify the reliability of the incident themselves.
Previously, crypto alerts had to be verified by security analysts before they were sent to customers. However, with the launch of this new feature, the wait time between when an incident occurs and when customers are alerted has been significantly reduced.
Since the Blockworks Monitoring feature combines real-time data with proprietary training developed by analysts over more than five years, the accuracy and speed with which these alerts are sent are unmatched.
According to Blockworks, the launch of this feature is aimed at building further trust in the on-chain markets, especially for crypto institutions whose work depends on trust.
The launch of Blockworks’ alert feature comes shortly after Brazil’s central bank launched a system that monitors crypto-related threats and issues alerts in real time.
Still on launches, Worldpay, formerly Worldcoin, has launched a self-custodial financial super app that combines stablecoin payments, trading, yield, virtual accounts, and portfolio tools into one app.
The app, which will be made available in more than 150 countries across eight currencies, will allow users to fund their accounts and send digital assets via their World usernames.
S&P Global to Acquire Blockchain Security Firm OpenZeppelin

S&P Global, the leading financial information services company, has agreed to acquire blockchain security company OpenZeppelin for an amount that has yet to be disclosed.
According to an S&P press release, the acquisition is aimed at complementing the company’s global risk assessment and ecosystem development capabilities in the digital asset market.
The deal will also enable S&P Global to create the next generation of on chain security assessments and benchmarks while delivering essential intelligence, especially as the capital market moves on chain.

"Our digital assets strategy centers on bringing trusted data, benchmarks and transparent risk assessment to markets as they move on chain," said Yann Le Pallec, President of S&P Global Ratings.
"As digital assets and tokenized markets continue to mature, OpenZeppelin's technology and expertise will complement our smart contract and on-chain technology risk assessment capabilities, giving traditional financial institutions and DeFi native companies alike the confidence to build and transact in this new environment."
Although the terms of the transaction have yet to be disclosed and the deal remains subject to closing conditions, OpenZeppelin will continue to operate under the OpenZeppelin name, with its CEO, Demian Brener, leading the company.
About OpenZeppelin
Founded in 2015, OpenZeppelin is a leading blockchain security firm that promotes secure development practices for teams aiming to build safely and securely on-chain.
Prior to this acquisition deal with S&P Global, OpenZeppelin had achieved several milestones, including launching OpenZeppelin Contracts, the first major open-source smart contracts library that eventually became the de facto industry standard for secure smart contracts.
The firm also pioneered professional smart contract security audits, which audited over $37 trillion in cumulative value, while also conducting over 900 security audits that identified more than 10,000 vulnerabilities.
OpenZeppelin powers 9 of the top 10 stablecoins, including Circle USDC, Ripple RLUSD, PayPal USD (PYUSD), Ethena USDe, BitGo USD1, and 10 of the top 10 tokenized funds, including BlackRock BUIDL, Centrifuge Anemoy JTRSY, Circle USYC, and Ondo OUSG and USDY.
Monad Proposes Wallet Upgrade to Protect Against Quantum Attacks and Lost Keys

Monad, the high-performance EVM-compatible Layer-1 blockchain, has published a proposal aimed at giving users greater flexibility and changing how blockchain wallets manage authentication.
The proposal, titled “Flexible and Upgradeable Account Authentication,” was published by Kushal Babel and Jan Camenisch, two senior researchers at Category Labs, the engineering team behind Monad.

At its core, the proposal has one goal: to separate a wallet’s permanent address from the credentials that control it, thereby giving users the flexibility to add, replace, or retire keys without having to change the wallet’s address or move assets.
By publishing the proposal, Monad aims to address a key problem with current blockchain wallets. Since most wallet addresses are permanently derived from a single secp256k1 public key, losing the corresponding private key can make the wallet account unrecoverable.
As a solution to this problem, Monad is proposing an AuthConfig model, where every wallet account holds a mutable AuthConfig. This allows an account to hold multiple authenticators and a separate reconfiguration policy, enabling users to access their wallet accounts even if a private key is lost. At launch, the supported schemes will include secp256k1, P-256, Ed25519, WebAuthn/passkeys, ML-DSA (post-quantum), and a ZK-OAuth verifier.
Although there is currently no quantum computer capable of breaking the cryptographic schemes used by crypto wallets, several reports have projected that this could become possible in the future.
In addition to Monad, other companies, including Ledger and Coinbase, have also taken steps to develop quantum-resistant wallets. Coinbase has established an independent Quantum Advisory Council while also developing a post-quantum security roadmap.
Ledger has also added ML-KEM and ML-DSA, two NIST-standardized post-quantum cryptographic algorithms, to its Ledger SDK as part of its efforts to develop quantum-resistant wallet technology.
Term Labs Loses $8.5 Million in Governance Exploit

Blockchain protocol Term Labs has lost an estimated $8.5 million after suffering a governance exploit that allowed hackers to gain control of the protocol’s vaults and drain funds.
According to blockchain security firm PeckShieldAlert, the attackers first built up enough voting power to take full control of four of the five USDC vaults and approximately 91% of the protocol’s Ethereum Meta vaults.

With this much voting power, the attackers were able to pass proposals, eventually enabling them to drain approximately 2,843 ETH, worth $6.87 million, and an additional $1.68 million in funds.
In response to the exploit, Term Labs acknowledged the incident. Although the team said it would share more details as the incident is being investigated, it advised all of its customers, as a safety precaution, to revoke all approval contracts associated with the protocol.
Governance exploits, which often involve attackers gaining enough voting power to execute malicious proposals, have become increasingly prevalent in recent times.
Prior to the Term Labs exploit, BonkDAO, a decentralized autonomous organization, also lost an estimated $20 million to $21 million from its treasury after attackers spent roughly $4.4 million buying enough BONK tokens to gain control of the votes and pass malicious proposals.
Summer Finance Hit by $6 Million Exploit

Summer Finance, a DeFi yield optimization protocol, was hit by an exploit that affected the protocol's USDC vaults, resulting in an estimated loss of roughly $6 million.
The exploit was confirmed by several blockchain security firms, including Blockaid, Cyvers, and CertiK. According to Cyvers, the attack appears to have been caused by the exploitation of a shared accounting vulnerability. The stolen funds were eventually swapped for the DAI stablecoin and transferred to the attacker's wallet.
Although all vaults across the Lazy Summer Protocol were immediately paused after the exploit was confirmed, the team later released a post-mortem report detailing how the attack occurred, its scope and impact, the response actions taken, and ongoing fund recovery efforts.

Image credit: x.com
According to the post-mortem report, the exploit targeted two Lazy Summer Protocol USDC vaults on the Ethereum mainnet. The attack, which is believed to have been planned over a period of about 3 months, was executed using a $65 million flash loan. Of that amount, approximately $64.8 million was deposited into Summer's vaults.
The attacker then deposited Varlamore USDC (vgUSDC) Growth tokens, which were essentially worthless, into the vulnerable Silo Ark vault, which had been partially shut down. Because the vault's accounting logic incorrectly treated the fake vgUSDC tokens as legitimate assets with real value, the attacker was able to withdraw genuine funds from the protocol.
In response, the Summer Finance team took several measures to contain the impact, including pausing vaults across the Ethereum, Base, Arbitrum, and Sonic networks. The team has also launched an investigation and begun tracing the stolen funds.
The Summer Finance exploit occurred around the same time that the BonkDAO treasury was drained of approximately $20 million. In that incident, the attacker reportedly purchased $4.4 million worth of BONK tokens, allowing them to meet the DAO's low quorum threshold. The attacker then passed a malicious governance proposal, BIP 76, which automatically transferred approximately $20 million from the treasury.
Humanity Protocol Pivots to Enterprise AI After $36 Million Hack

Humanity Protocol, the blockchain-based decentralized identity (DID) project, is pivoting toward enterprise AI following the June exploit that drained $36 million from the protocol's treasury.

Image credit: youtube.com
The pivot was revealed by the protocol's founder, Terence Kwok, on The Block's daily show, "The Starting Block." According to Kwok, the team had spent the last couple of months rethinking its direction, but the hack accelerated a shift that was already underway.
"I think, in light of the hack, we're probably moving forward by repositioning ourselves less as a blockchain company or an identity or decentralized ID project," Kwok told Gareth Jenkinson, anchor of The Block's daily show, during the interview.
As part of the repositioning, Kwok said the Humanity Protocol team would focus on building products and services tied to enterprise AI. According to him, identity will only become more relevant in a world increasingly shaped by AI.
Kwok also pushed back against earlier claims that the hack was a rug pull orchestrated by the team. In the aftermath of the exploit, on-chain investigator ZachXBT said the incident was "possibly staged" and that he was "not buying the team's story."
ZachXBT claimed the team had been "crime pumping" the protocol's H token for weeks and that the exploit was the best way for active market makers to exit. However, after analyzing on-chain evidence and laundering flows, he revised his assessment, concluding that the hack was caused by a private key compromise.
How the Hack Happened
The Humanity Protocol hack was caused by a serious operational security failure. The laptop of one of the protocol foundation members was compromised. Because the laptop contained multiple Gnosis Safe multisig keys, the attacker obtained enough signatures to gain control of the protocol's Hyperlane bridge ProxyAdmin.
Once granted admin privileges, the attacker drained the existing H tokens from the protocol's wallets and bridges. The attacker also upgraded contracts and minted roughly 200 million additional H tokens across Ethereum and BNB Chain.
As a result, about $36 million worth of H tokens, the protocol's native cryptocurrency, was lost. The H token also crashed by nearly 90%, falling from about $0.67 to $0.85 to as low as $0.05 to $0.13.
StablR Stablecoins Lose Peg After $10M Wallet Exploit

EURR and USDR, stablecoins issued by StablR, have each lost their euro and dollar pegs following an exploit on StablR’s multisignature wallets.
The exploit, first flagged by on-chain sleuth ZachXBT, led to losses of about $10 million. According to ZachXBT, two contracts tied to StablR were exploited, with the attacker funding their wallet through Circle’s Cross Chain Transfer Protocol (CCTP) on Noble.
In a further update on his Telegram channel, ZachXBT said he had helped freeze six figures worth of the stolen funds, while adding that the StablR team appeared to be inactive as the attack was still ongoing three hours after he raised the alarm.
Blockchain security company Blockaid also detected the exploit, attributing the compromise to a private key issue in StablR multisignature wallets. According to Blockaid, the attacker gained access to one of StablR’s three multisignature wallets.
Since the multisignature wallet had a threshold of 1 out of 3, the attacker, after gaining admin access, replaced the other two legitimate owners. The attacker then minted 8.35 million USDR and 4.5 million EURR stablecoins and swapped them on decentralized exchanges. Blockaid further stated that the attack was not a smart contract bug, but instead a key management and governance failure.
A few hours after the incident was flagged, the StablR team issued a security update stating that they were actively working to contain and minimize the impact of the hack.

At the time of writing, EURR, StablR’s euro-pegged stablecoin, had lost about 53 percent of its value, dropping to about $0.54 according to CoinGecko. USDR, the stablecoin pegged to the US dollar, had risen slightly to $0.99.
This is not the first time a protocol has lost its stablecoin peg due to a governance exploit. In March of this year, Resolv Lab suffered a governance exploit that enabled attackers to gain admin access and mint roughly $80 million worth of Resolv’s USR, a dollar-pegged stablecoin.
Due to this uncontrolled minting, the USR stablecoin lost its peg to the US dollar, crashing to roughly $0.05 within minutes. USR is currently trading at $0.16 according to CoinGecko.
Attempted Kidnapping Targets Sandbox Co-Founder’s Wife

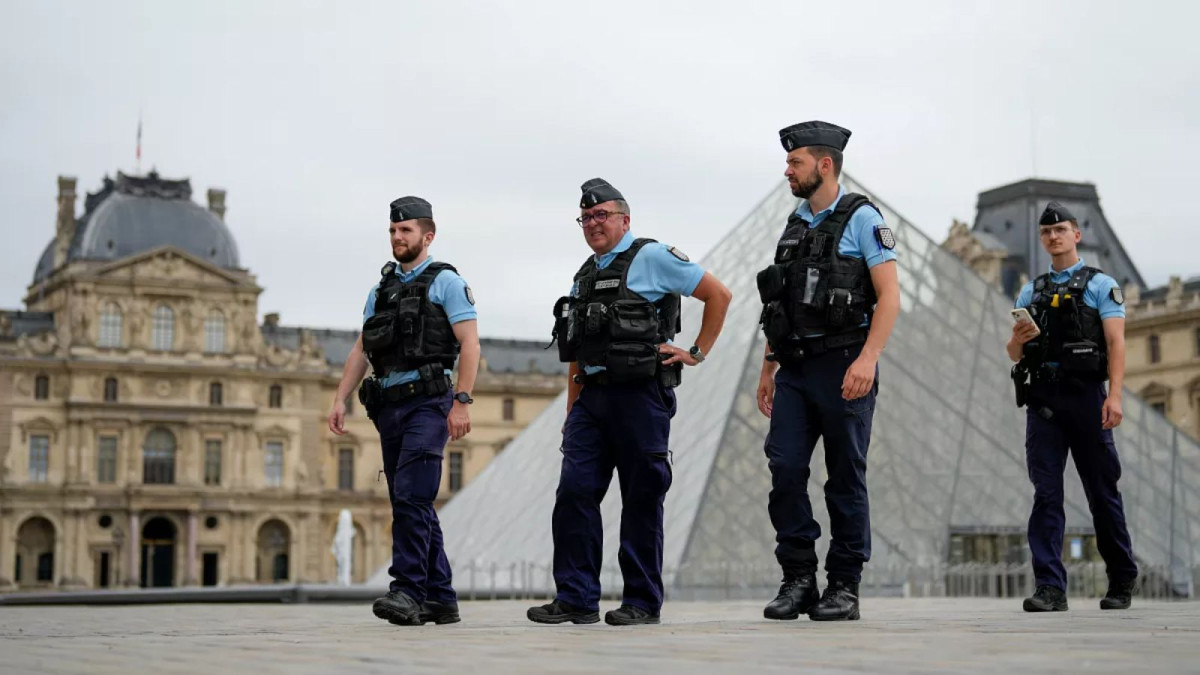
The wife of Sébastien Borget, co-founder and chief operating officer of The Sandbox, an Ethereum-based virtual world platform, reportedly narrowly escaped being kidnapped at the couple’s home in Villenoy, Seine-et-Marne, France, this week.
According to Le Journal du Dimanche, a local French newspaper, one of the kidnappers disguised as a deliveryman wearing a branded vest, knocked on the couple’s home.
On opening the gate, five other hooded accomplices charged at Borget’s wife in an attempt to forcefully drag her into a vehicle. However, her cries alerted neighbors, forcing the group to scatter and leave the victim behind.
Four suspects escaped in the vehicle, while two others fled on foot and hid nearby. The two suspects attempted to book a ride-hailing car but were later captured by officers from the Meaux Anti-Crime Brigade.
The two suspects arrested were identified as Mateo V. and Walid H., reportedly born in 2010 and 2009, respectively, and are both residents of Pantin in Seine-Saint-Denis. They were found carrying a fake handgun, zip tie restraints, and balaclavas.
While investigations are ongoing, local news reports have linked the attempted kidnapping to cryptocurrencies, citing an increase in crypto-related wrench attacks and kidnapping incidents reported this year.
France Remains a Hotspot for Crypto Wrench Attacks
There has been an increase in attacks on crypto holders, with France leading and becoming the global epicenter.
In just the first four months of this year, between 41 and 47 incidents were reported in France, an average of one incident every 2.5 days. The French authorities have also charged 88 suspects, including more than 10 minors, across 12 major investigations, with 75 in pretrial detention.
Jameson Lopp, cofounder and chief security officer of Casa, a well-known blockchain security company, has long been tracking these crypto-wrench attacks in a GitHub repository named "physical bitcoin attacks." According to the repository, there have been about 35 recorded incidents this year, with France accounting for 74 percent of those, or 26 incidents in total.
To help combat the increasing number of wrench attacks, Binance recently added a withdrawal protection feature to the Binance wallet that activates a lockdown period, preventing withdrawals from the wallet, especially by intruders.
THORChain Halts Trading After $10M Exploit

THORChain, the decentralized cross-chain liquidity protocol that enables asset swaps between blockchains, has paused trading on its platform following reports by security researchers, including ZachXBT and PeckShield, that the platform was exploited for more than $10 million.

Following alerts from security researchers, THORChain halted all trading activities, citing abnormal and suspicious behavior it had detected. According to the team, one of its six Asgard vaults was compromised, resulting in a loss of approximately $10 million.
However, the team said in a post on X that user funds were safe and that only protocol-owned funds were affected.

“Investigation is still ongoing to determine the root cause. Contributors are actively working on the issue and we will report updates as we progress toward a solution,” the team said.
“We are asking all node operators to immediately review their infrastructure, hosts, key management systems, and operational security for any signs of compromise or abnormal behavior, and to report anything suspicious in Discord.”
Following the team's confirmation of the exploit, RUNE, the native crypto asset of THORChain, fell by nearly 15%, wiping out more than $27 million in market capitalization. Its market capitalization dropped to around $182 million. At the time of writing, RUNE was trading at $0.50, down 13.8% from its pre-hack price of $0.58.
Latest of Several Attacks
This is not the first time THORChain has been exploited by attackers. In 2021, it suffered three separate exploits, resulting in losses of over $16 million.
In the first exploit, it lost approximately $350,000 due to a vulnerability in the way the protocol handled ERC-20 deposits. In the second exploit, which occurred just one month after the first, THORChain suffered losses of between $4.9 million and $8 million. In the third exploit, the protocol lost about $8 million due to a refund logic vulnerability.
The THORChain exploits are among the latest and largest of the 11 decentralized finance exploits recorded this month. Exploits in decentralized finance remain widespread, with the previous quarter recording more incidents than the first quarter of 2025.
Volo Protocol Hack Drains $3.5M From Sui-Based DeFi Vaults

Volo Protocol, a decentralized finance protocol built on the Sui blockchain, has suffered a security breach that led to the loss of approximately $3.5 million in digital assets.
In an effort to maintain transparency, the team in an X post on Wednesday publicly announced the security breach. According to the team, the attack only affected assets in selected vaults, including Wrapped Bitcoin (WBTC), Matrixdock Gold XAUm, and USDC (USDC).

On detecting the breach, the team said it acted quickly to contain it and minimize further damage. It stated, “We detected the attack, immediately notified the Sui Foundation and ecosystem partners to contain the damage, and froze the vaults to prevent any further exposure.”
As of the time of its first reporting on the incident, the Volo team said that the $28 million in total value locked across other vaults was safe, adding that all vaults on the protocol were temporarily frozen pending a full postmortem and remediation. The team also said it was in damage control mode and was actively working with on chain investigators and ecosystem partners to recover the stolen funds.
The team released updates on the hack
Since the hack happened, the Volo team has, in three separate updates, transparently informed the community about the efforts being made to recover the stolen funds.
In the first two updates, the team said it was already working with ecosystem partners and had successfully frozen approximately $500 million of the stolen funds, while also intercepting and blocking the hacker’s attempt to bridge 19.6 WBTC. According to the Volo team, these funds were no longer under the hacker’s control.
In a third update, the team said it had already frozen $2 million of the stolen funds, and that together with ecosystem partners and security teams, it had flagged the hacker’s EVM addresses across the majority of centralized exchanges, swappers, and KYC tools.
The Volo protocol hack came shortly after the KelpDAO exploit and the Drift Protocol exploit, which led to a combined loss of over $570 million, and are currently the largest DeFi hacks that have occurred this year. So far, over $770 million has been lost to DeFi hacks this year.
Solana Foundation Moves To Strengthen Its Ecosystem Security

The Solana Foundation, in collaboration with blockchain security firm Asymetric Research, has launched new security initiatives aimed at strengthening the security of the Solana network.
In a blog post on Monday, the foundation announced the launch of new security initiatives designed to provide an extra layer of protection for protocols built on the network. Among these initiatives are STRIDE, a security framework, and SIRN, a network of security firms focused on protecting the Solana ecosystem.

The STRIDE Framework
STRIDE, which stands for Solana Trust, Resilience and Infrastructure for DeFi Enterprises, is a structured security framework and program launched by the Solana Foundation. It is aimed at evaluating, monitoring, and escalating security across all projects built on the Solana network.
The STRIDE framework is built on eight key pillars: program security, governance and access control, oracle and dependency risk, infrastructure security, supply chain security, operational security, monitoring and incident response, and log management and forensics.
These pillars will be used by the foundation’s partner, Asymmetric Research, to evaluate the security strength of all protocols on the Solana blockchain. Protocols with a total value locked of more than $10 million that pass the STRIDE evaluation will receive continuous operational security and active threat monitoring, funded by Solana Foundation grants. The higher the evaluation result, the greater the level of protection and funding they will receive.
Protocols with a total value locked of more than $100 million that pass the STRIDE evaluation will also receive, in addition to grants, formal fund verification. The foundation describes this as a mathematical, proof based method that exhaustively guarantees the correctness of smart contracts.
The findings of the STRIDE framework will be published publicly. According to the foundation, this is intended to give users and investors insight into the protocols they use and rely on.
SIRN: A Network of Security Firms
Among the initiatives launched by the Solana Foundation is SIRN, short for Solana Incident Response Network, a network of security firms that will respond and act in the event of a security incident.
Although SIRN will be available to all blockchain protocols on the Solana network, priority will be given to protocols with higher total value locked, similar to the additional benefits that protocols with higher total value locked will receive under the STRIDE program.
Interested in knowing who makes up SIRN?
The Solana Incident Response Network comprises Asymmetric Research, OtterSec, Neodyme, Squads, and ZeroShadow, a combination of cybersecurity firms that includes Web3 and traditional security firms as well as a smart contract auditing firm.
Increase in DeFi attacks
The programming initiatives launched by the Solana Foundation are in response to the over $280 million attack on Drift Protocol, the largest decentralized perpetual exchange on the Solana blockchain. The attack is, so far, the most devastating DeFi attack this year and the second largest in the history of the Solana blockchain, following the 2022 Wormhole attack, which resulted in losses exceeding $325 million.
Step Finance, a DeFi aggregator built on Solana, was also affected by a DeFi hack earlier this year, which led to losses of about $40 million. According to DeFiLlama, over $168 million was stolen across 34 blockchain protocols in the first quarter of this year, prior to the Drift incident.